Blog
Engineering, product and guides from the Formal team.
Engineering
How we build Formal
Deep dives written by the engineers building Formal.
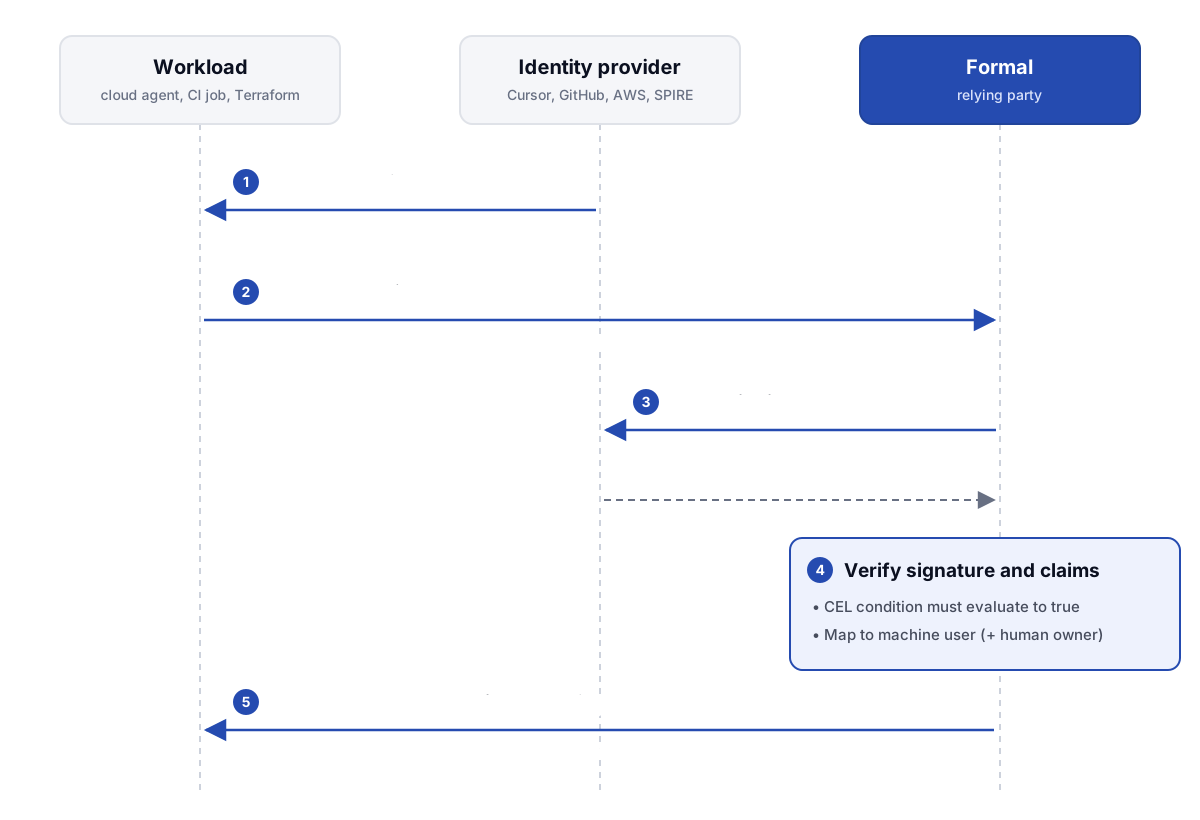
Giving Cloud Agents Production Access with OIDC, Not Secrets
How Formal uses OIDC to give cloud coding agents auditable, policy-controlled, short-lived access to production data and cloud infrastructure without long-lived secrets.
 Aditya Saligrama

PSA: fork() considered harmful in macOS
A macOS Network framework bug plus Go's fork/exec path can hang endpoint processes at 98% CPU. posix_spawn is the way out.
 Drew Gregory
The Metabase Zero Day and the Case for Enhanced Data-Layer Security
Lessons from the Metabase zero day, including how data access controls can limit exposure and support incident response.
Security Debt We Never Created
How Formal eliminates entire categories of security work through architectural choices.
Aditya Saligrama
Editing Code Visually Without Sacrificing Fidelity
Building a visual editor for Rego policies using AST parsing and WebAssembly.
 Faris Ashai
Using Proxies to Hide Secrets from Claude Code
How to use HTTP proxies to prevent credential exposure in Claude Code sandboxes.
Drew Gregory
Allowlisting Some Bash Commands is Often the Same as Allowlisting All with Claude Code
How allowlisting developer tools in Claude Code can inadvertently allow arbitrary command execution.
Drew Gregory
The Permission Pitfall: Securing MCP Servers Without Limiting Value
Why MCP servers need granular permission enforcement beyond native capabilities.
 Paul Yoo
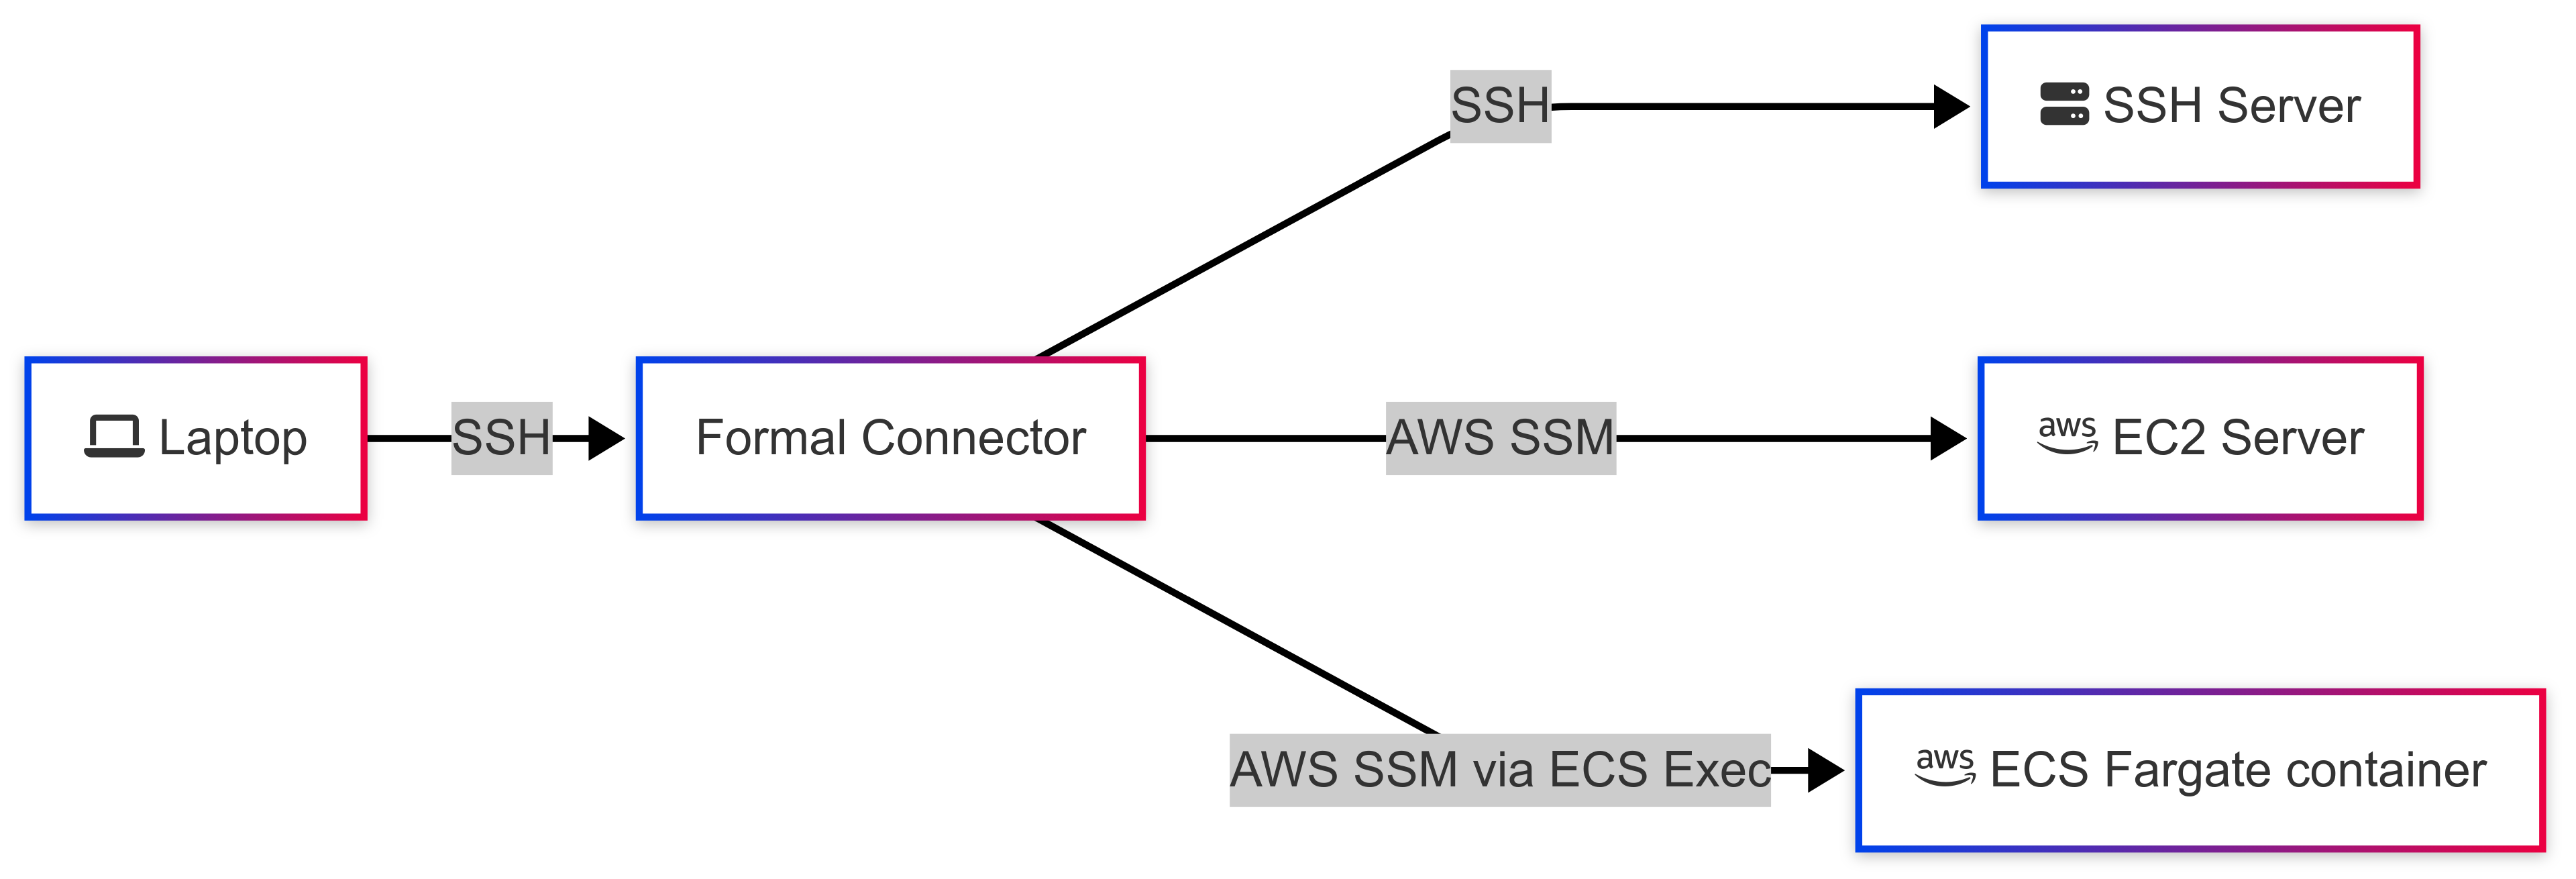
Down the Rabbit Hole: Implementing SSH Port Forwarding over AWS Session Manager
Implementing SSH port forwarding over AWS Session Manager with concurrency fixes.
Aditya Saligrama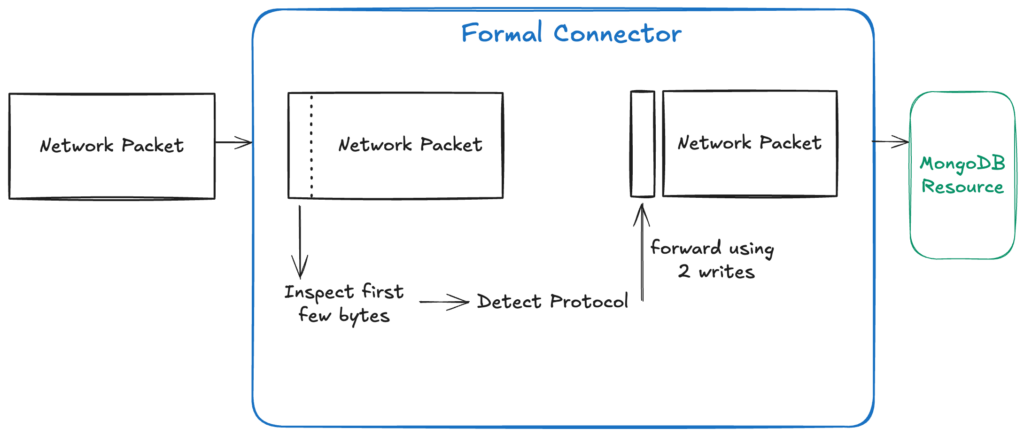
Building a Protocol-Aware Reverse Proxy: Lessons from Handling MongoDB's Unique Framing
How to handle MongoDB's unique message framing in a protocol-aware reverse proxy.
Product & company
What's new at Formal
Launches, product updates and company news.
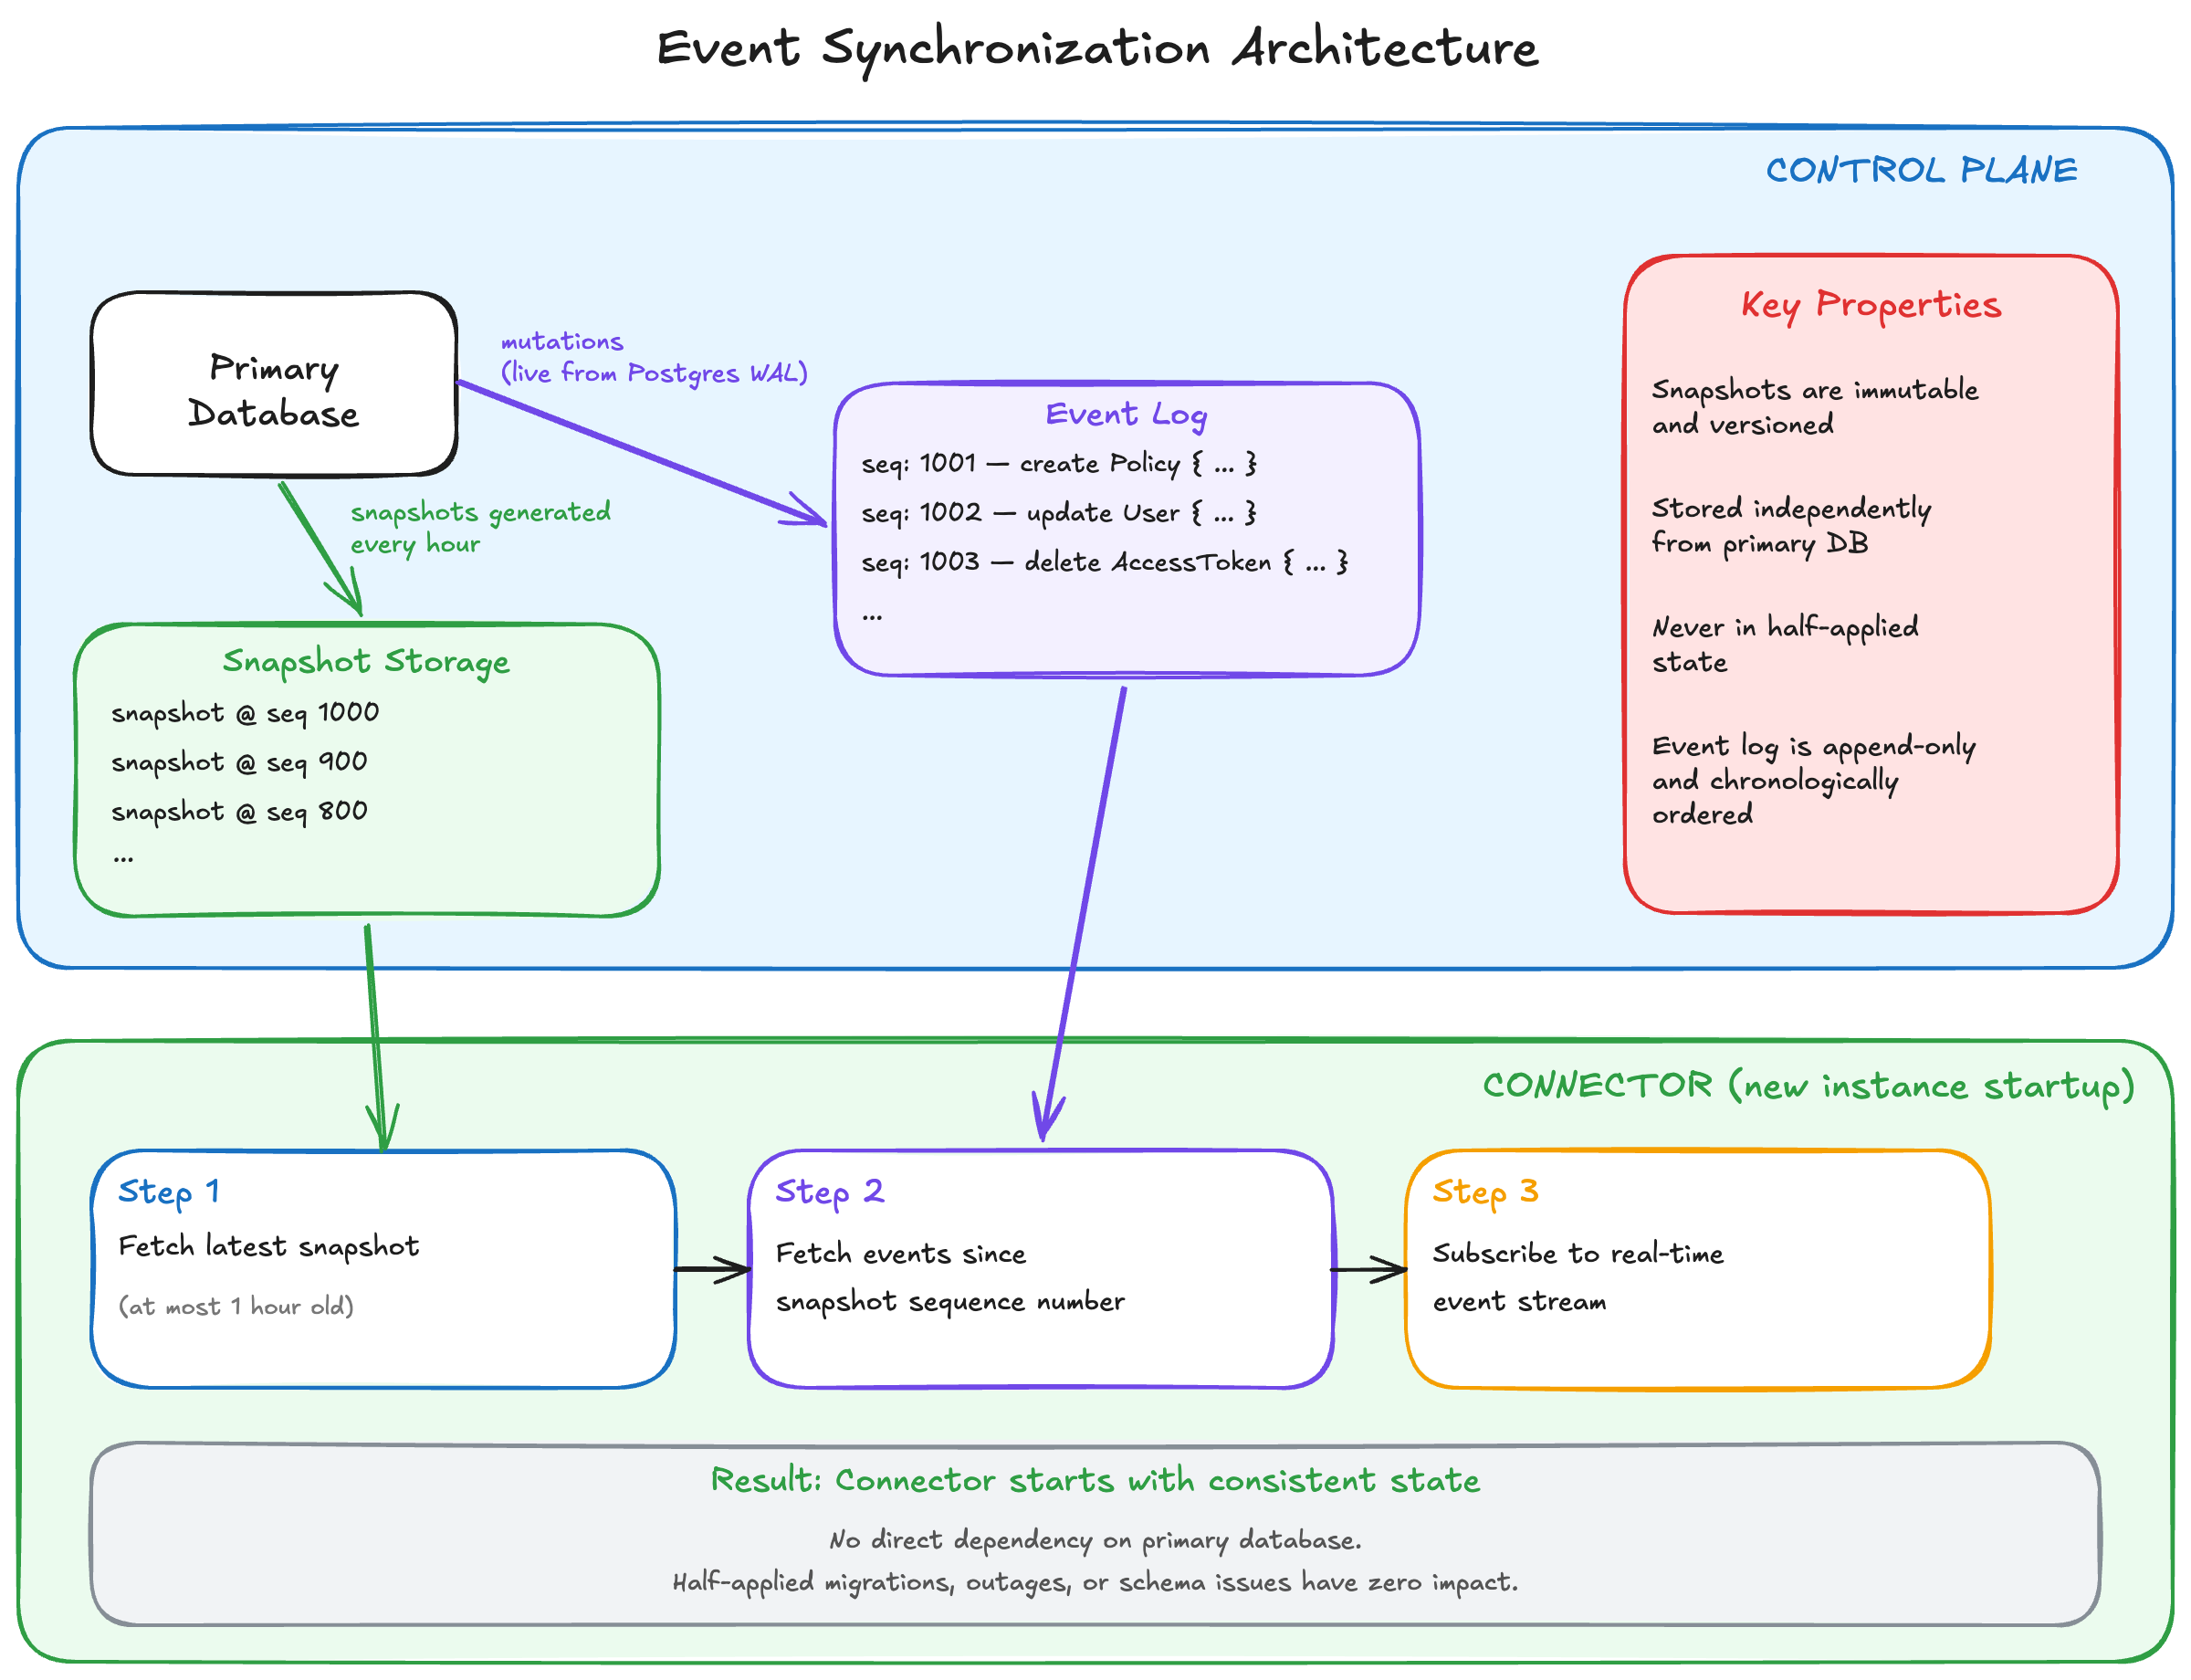
Announcing Connector v2.0.0
Version 2.0.0 of the Connector significantly improves data efficiency and reliability when synchronizing data with the control plane.
Aditya Saligrama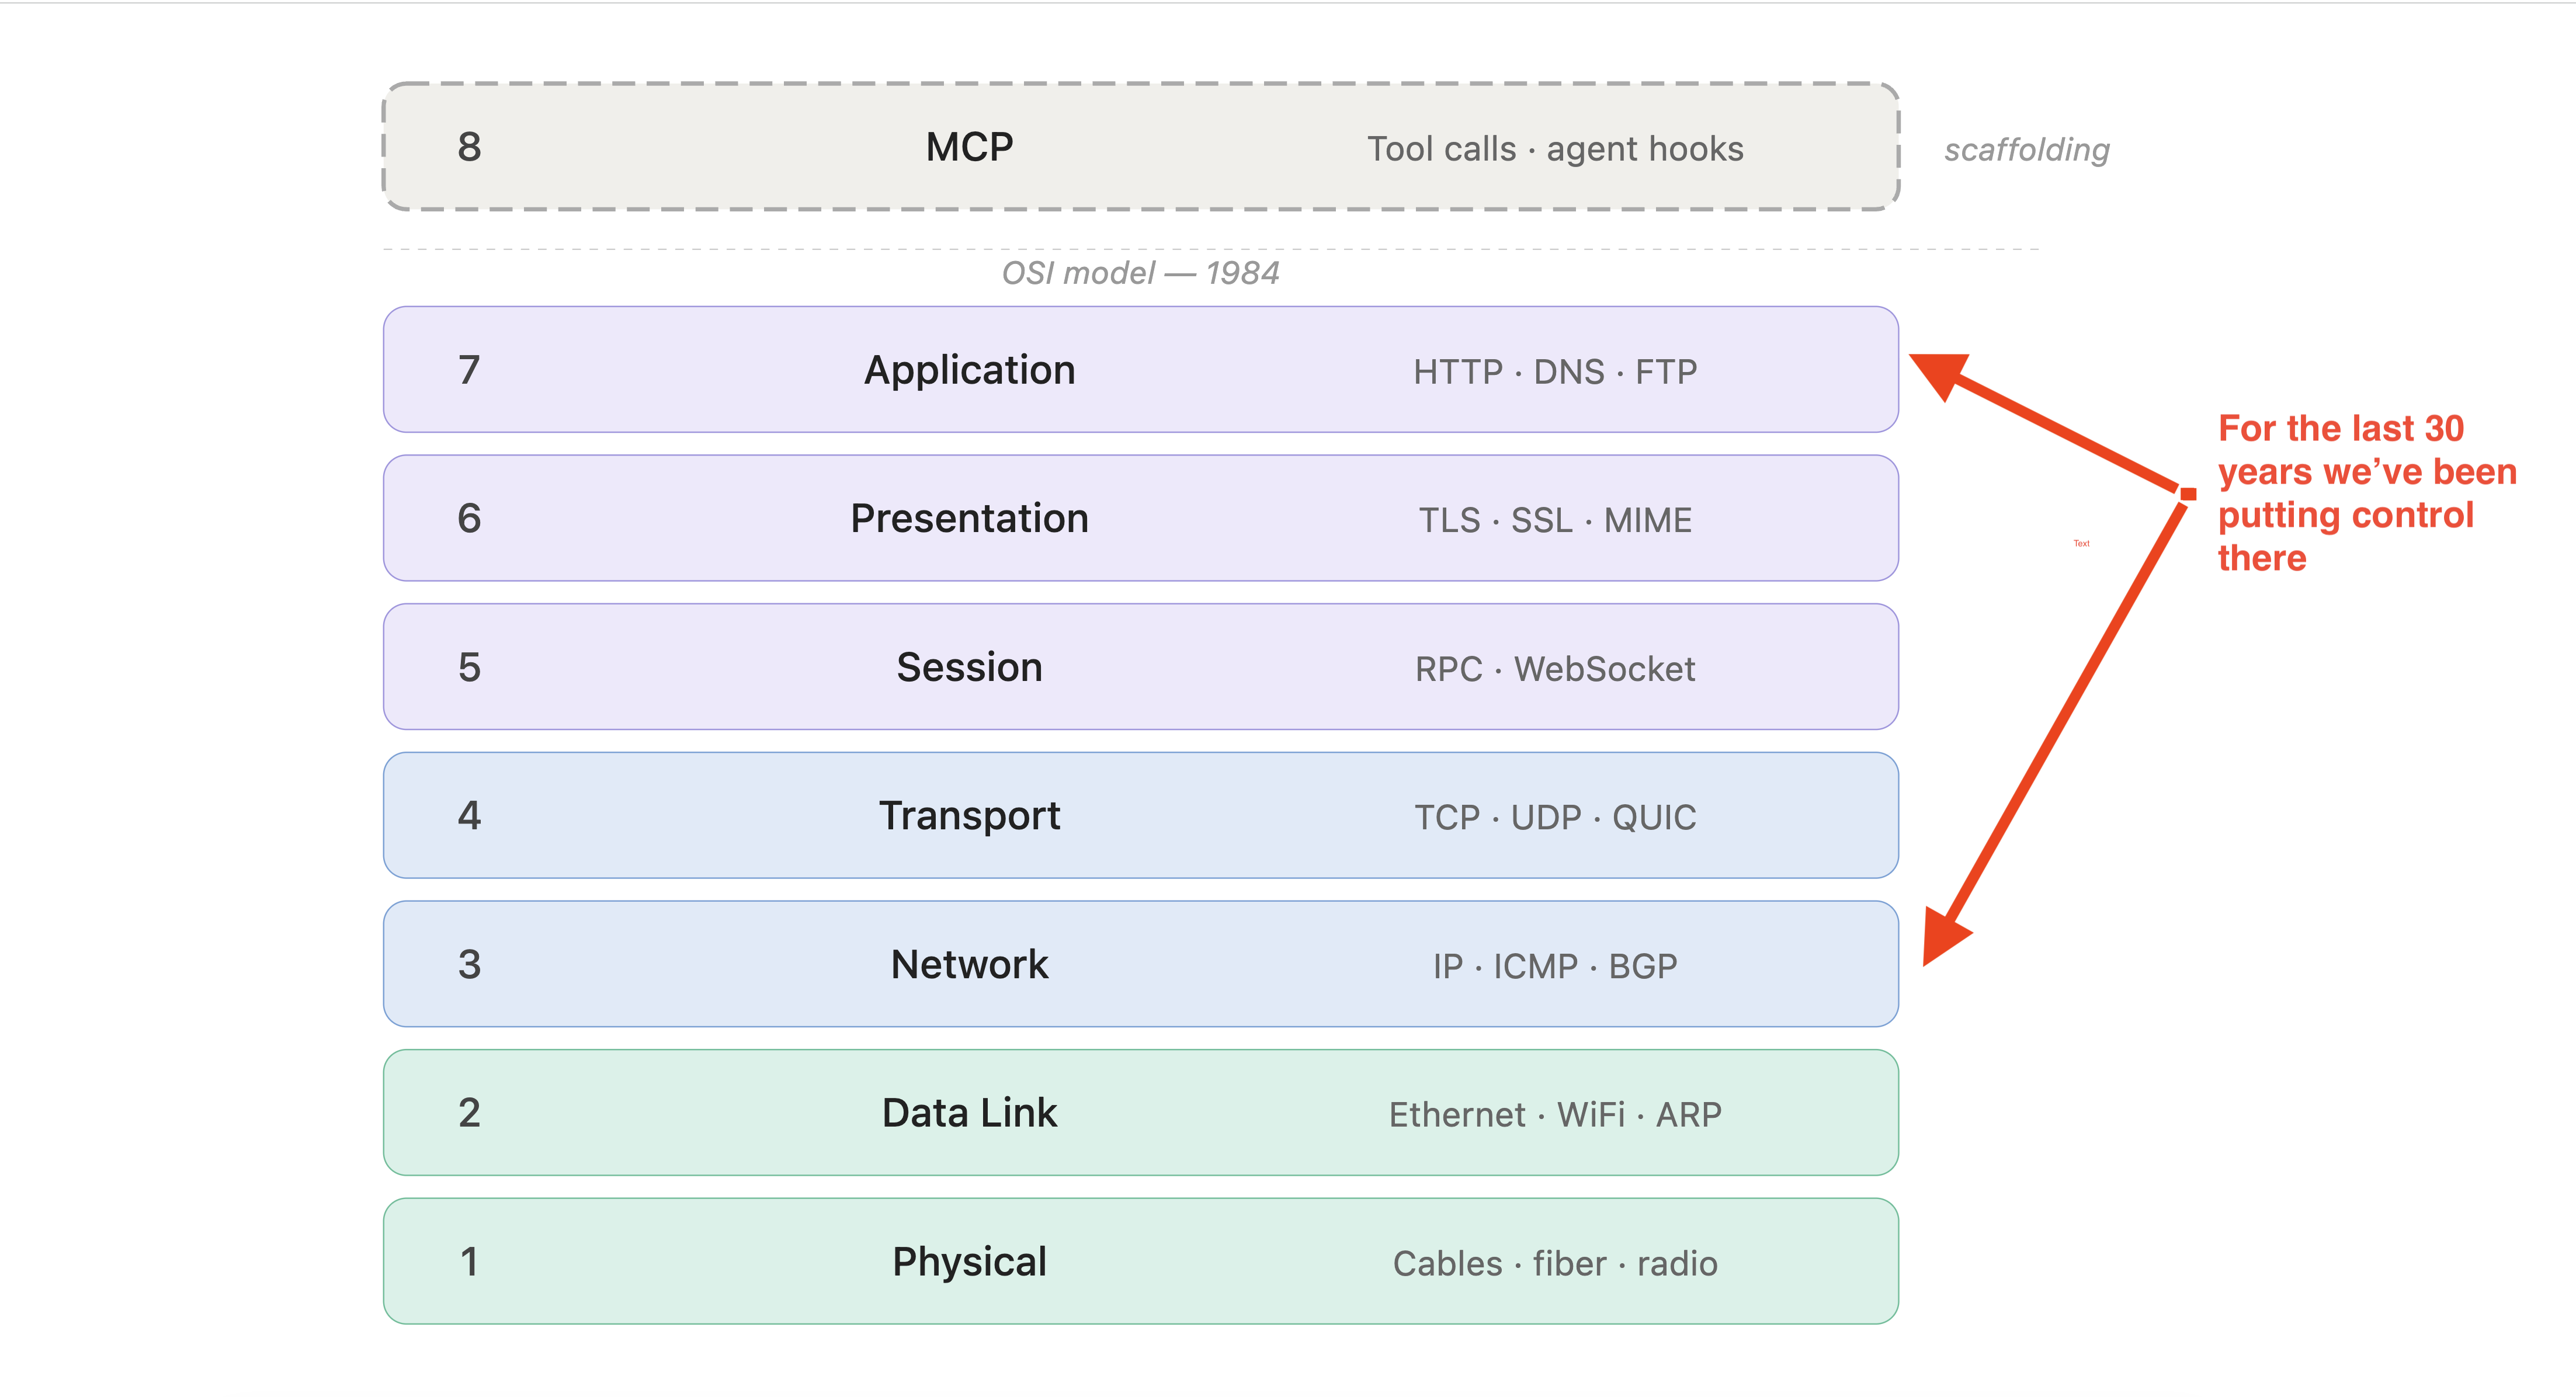
Stop Building Scaffolding: Who Cares About MCP vs CLI
The MCP vs CLI debate is missing the point. Both are scaffolding over temporary model limitations. The real problem is least-privilege enforcement.
 Mokhtar Bacha
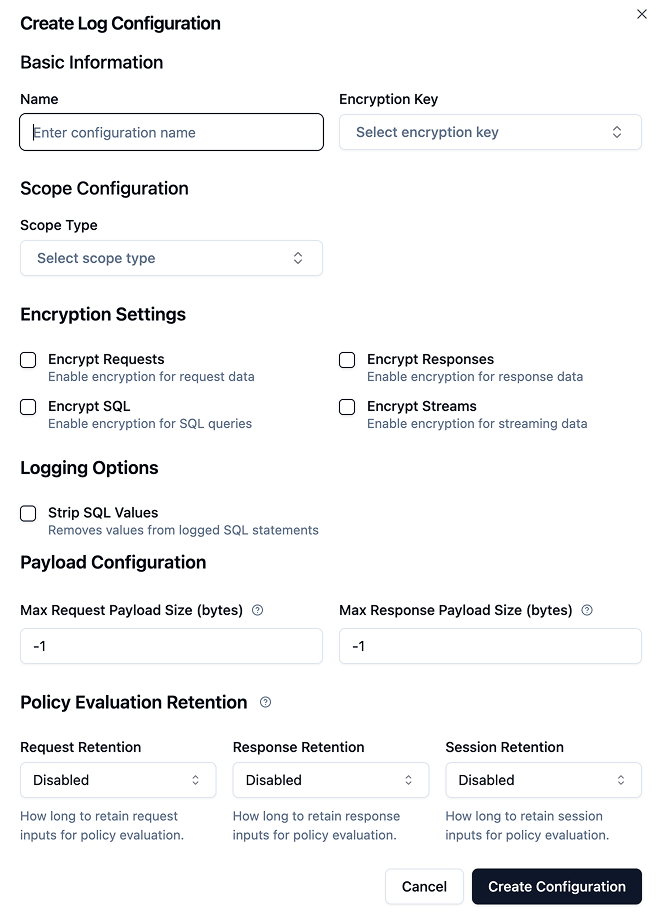
Introducing Fine Grained Control for Connector Logs
Introducing configurable log controls for encryption, retention, and data masking.
Mokhtar Bacha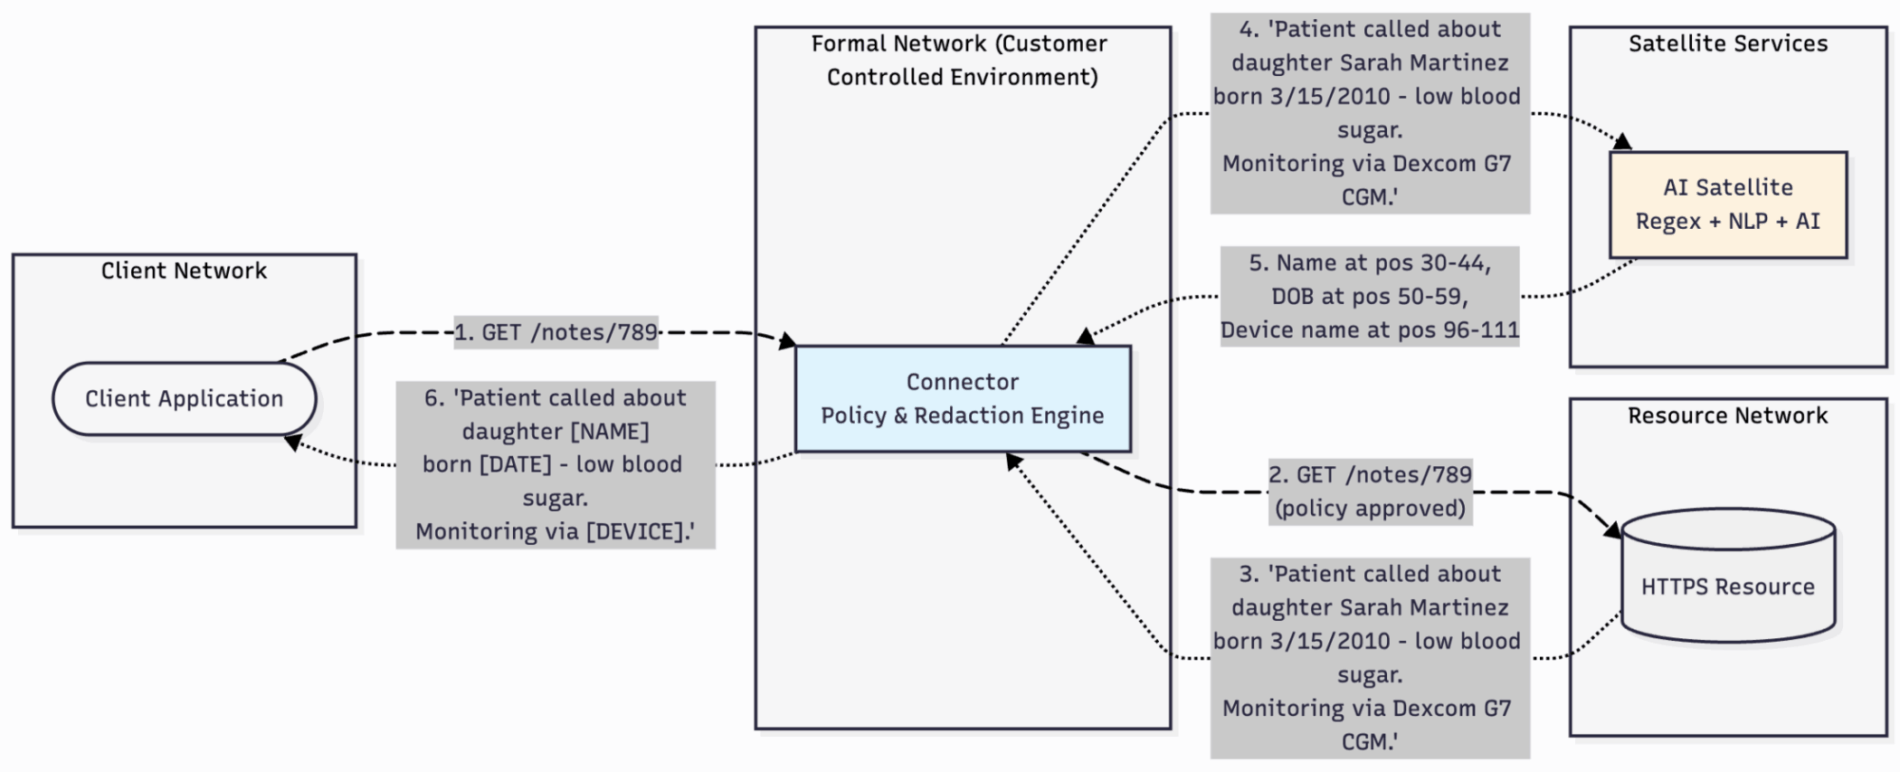
From Security Problem to Security Solution
Building a defense-in-depth PHI protection system for healthcare.
Formal Named Cloud Security Segment Leader in Latio Market Report
Formal recognized as Cloud Security Segment Leader in the 2025 Latio Market Report.
Mokhtar Bacha
Formal Comes Out of Stealth with $6.8M in Funding to Secure the Modern Data Stack
Formal announces $6.8M seed funding to secure the modern data stack.
Mokhtar BachaGuides
Securing AI agents, step by step
Practical guides for Claude Code, MCP and AI coding agents.
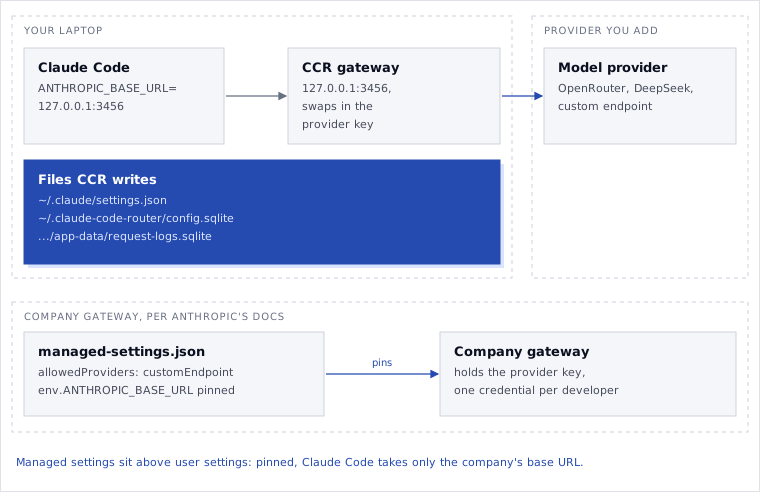
Claude Code Router Tested on a Work Laptop
Claude Code Router points Claude Code at OpenRouter, DeepSeek or a local model. We ran 3.1.3 on a Mac: the settings it writes, where keys and prompts go.
 Adrien Missioux
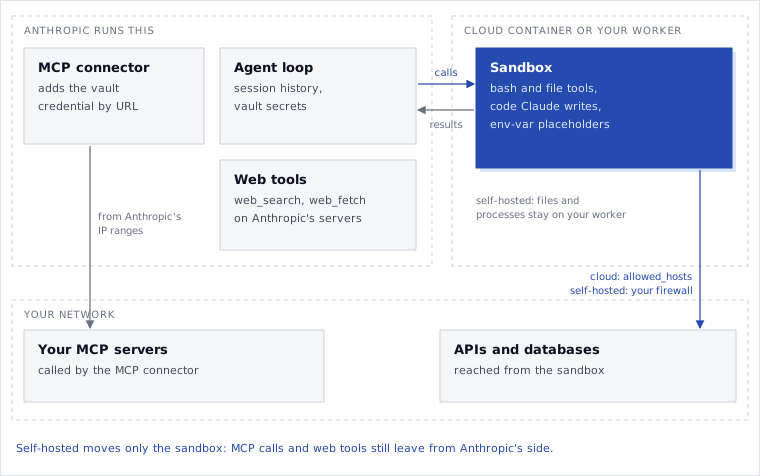
Claude Managed Agents: What Stays on You
Claude Managed Agents isolates each session and keeps vault secrets out of the sandbox. We probed the defaults: what Anthropic secures, what stays on you.
Adrien MissiouxClaude Code Hooks: I Tried to Get Past Them
I tested Claude Code hooks against npm test, go test, a dev server, a broken script and repo settings. What a PreToolUse hook stopped and what got past.
Adrien MissiouxMCP vs Skills: When to Use Each, Secure Both
MCP vs skills: MCP connects an agent to a system, a skill teaches it a procedure and can run scripts as you. When to use each, and how to secure both.
Adrien Missiouxdangerously-skip-permissions: Run It Safely
Claude Code dangerously-skip-permissions drops every prompt but deny rules. What still applies, and how to run YOLO mode with egress policy and no keys.
Adrien MissiouxClaude Code Sandbox: Setup and Blind Spots
How to turn on the Claude Code sandbox, what it still lets through (reads of ~/.ssh, pushes to allowed hosts, unread TLS) and the egress rules we add.
Adrien Missioux